Generic Interface
An abstract model built from zones, hosts and services. It hides port numbers and is suited to personal firewalls and small networks.
Screenshots
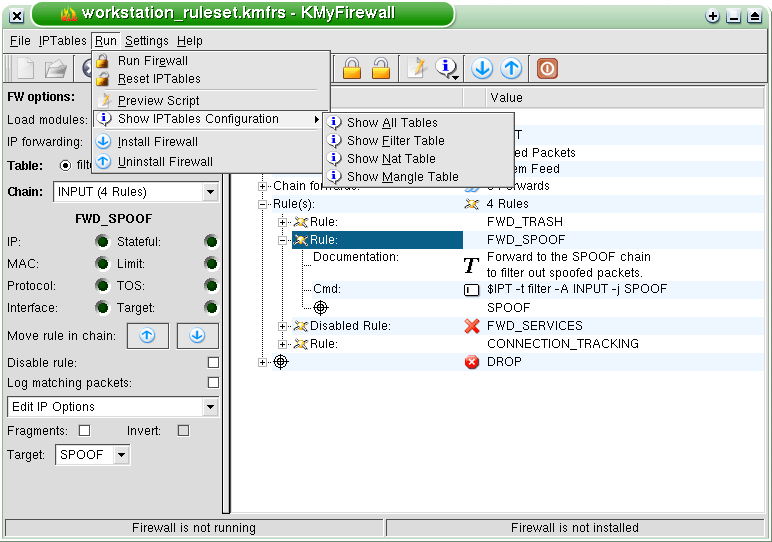
KMyFirewall ships with two editors. The Generic Interface works with zones and hosts. The IPTables Interface exposes chains, matches and targets. The screenshot below is from the IPTables Interface in the 1.1 series.
A workstation ruleset with SPOOF, FWD_TRASH and FWD_SERVICES chains.
An abstract model built from zones, hosts and services. It hides port numbers and is suited to personal firewalls and small networks.
A direct view of chains, rules, matches and targets. It is built for administrators who need exact control over the generated ruleset.
The interface runs in the KDE Desktop Environment and generates rules for IPTables on Linux. Background: KDE and IPTables.