Screenshots · IPTables Interface
Every chain, rule and target in view.
The IPTables Interface is a close representation of the ruleset your configuration will create. It is meant for experienced administrators who need fine grained control.
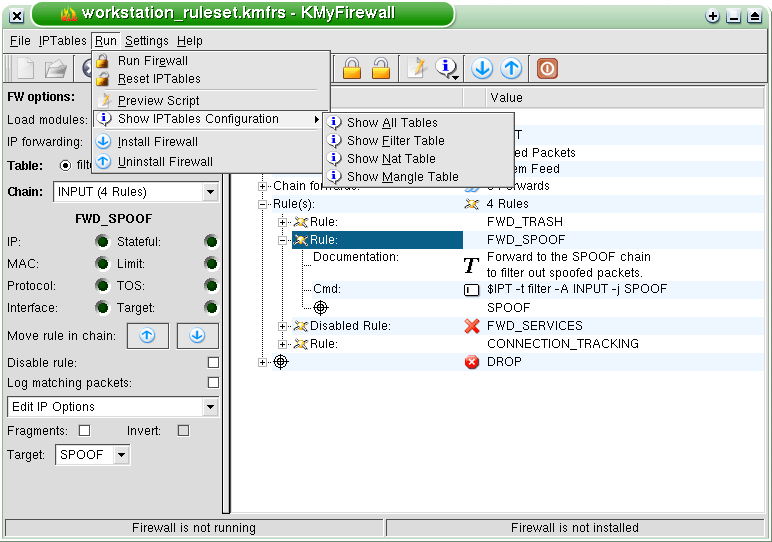
The workstation ruleset view
Release 1.1 series, IPTables Interface.
What the screenshot shows
The window title names the document workstation_ruleset.kmfrs. The left side holds the rule editor, with options for stateful matching, MAC addresses, limits, protocol, TOS, interface and target.
The right side shows the chain structure of the current document. The visible chains include SPOOF, FWD_TRASH, FWD_SERVICES and CONNECTION_TRACKING, with rules and targets such as DROP.
Interface notes
- Almost one to one representation of the IPTables ruleset.
- Rule option editors are provided by plugins.
- Supports stateful filtering, NAT, MANGLE, logging and user defined chains.
- Linux only, because it is bound to netfilter and iptables.
Read Using KMyFirewall and Filtering and manipulation of packets. Background: IPTables and KDE.